Learn how to manage Multi-Factor Authentication (MFA) using Google or Microsoft authenticator apps for your users.
USM Content
Where to start
This article is the starting point for managing authenticator app MFA across your plan. Depending on your task, you may also need these related articles:
- Configure the Require MFA setting to enforce MFA for all users on your plan.
- Exempt users from authenticator app MFA to exclude specific users from MFA enforcement.
- Reset authenticator app MFA for users to allow users to re-enroll on a new device.
- Set up your authenticator app to access the end-user guide for enrolling in authenticator app MFA.
- Troubleshoot the authenticator app to see common issues and fixes for authenticator app setup and use.
System Admins can turn the authenticator app on or off as a second-factor authentication option (2FA) in the Admin Center.
MFA for non-SSO users is off by default for all existing plans created before October 30, 2025. New Enterprise plans sold, purchased, or activated after October 30, 2025, have MFA for non-SSO users turned on by default.
How authenticator app MFA pairs with sign-in methods
Use the authenticator app alongside a primary sign-in method. It can't serve as the only sign-in factor. The authenticator app automatically pairs with either email and password or email-based time-based one-time passcode (TOTP) as the primary sign-in factor. Because of this pairing, you can't enforce the authenticator app as a standalone sign-in method.
Supported apps
While technically compatible with any authenticator app, Smartsheet officially tests and recommends Microsoft Authenticator and Google Authenticator. Support from Smartsheet is limited to configurations involving these recommended applications.
What your users experience
When you enforce authenticator app MFA for a plan or domain, each affected collaborator sees an enrollment prompt at their next sign-in. The prompt walks them through linking their authenticator app to their Smartsheet account.
Collaborators can’t access Smartsheet until they’ve completed enrollment.
You can share the end-user setup guide with your organization so users know what to expect: Set up your authenticator app for signing in to Smartsheet.
Users excluded from MFA enforcement
System Admins can exempt individual users from the enforced MFA policy to accommodate edge cases, such as users with specific compliance challenges. You can manage these exemptions from the Edit user panel's More actions menu on the Seat types and true-up page (User Roles and Reports page in the legacy model) in Admin Center. Learn how to exclude specific users from the MFA enforcement.
Reset MFA for users
If a user loses their device or can’t access their authenticator app, you can reset their MFA enrollment via Admin Center, allowing them to re-enroll on a new device. Learn how to reset MFA for a user.
Only System Admins can perform this action; Group Admins or non-System Admin users lack this capability.
Activate authenticator app 2FA enforcement
System Admins on Business and Pro plans can only enable or disable the authenticator app enforcement at the plan level. However, System Admins on Enterprise plans can activate this feature at either the plan or domain level.
When the domain-level authenticator app is enforced, all users within the activated domain must set up their authenticator app during their next sign-in and use it for multi-factor authentication in future accesses.
Business and Pro plans
- Go to the Admin Center homepage.
- Scroll to the Settings section and identify the Authentication card.
Select Multi-factor authentication (MFA).
Brandfolder Image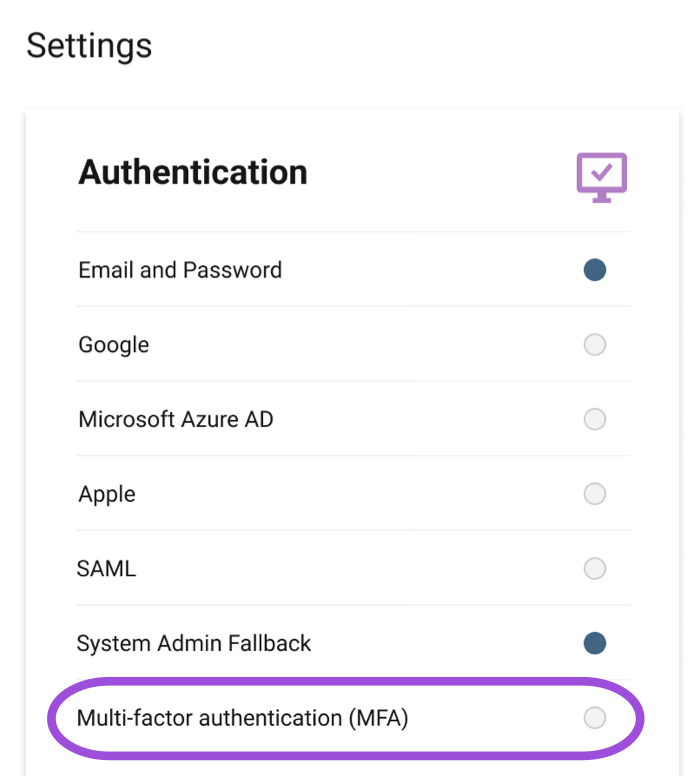
Select Turn on to confirm the action.
Brandfolder Image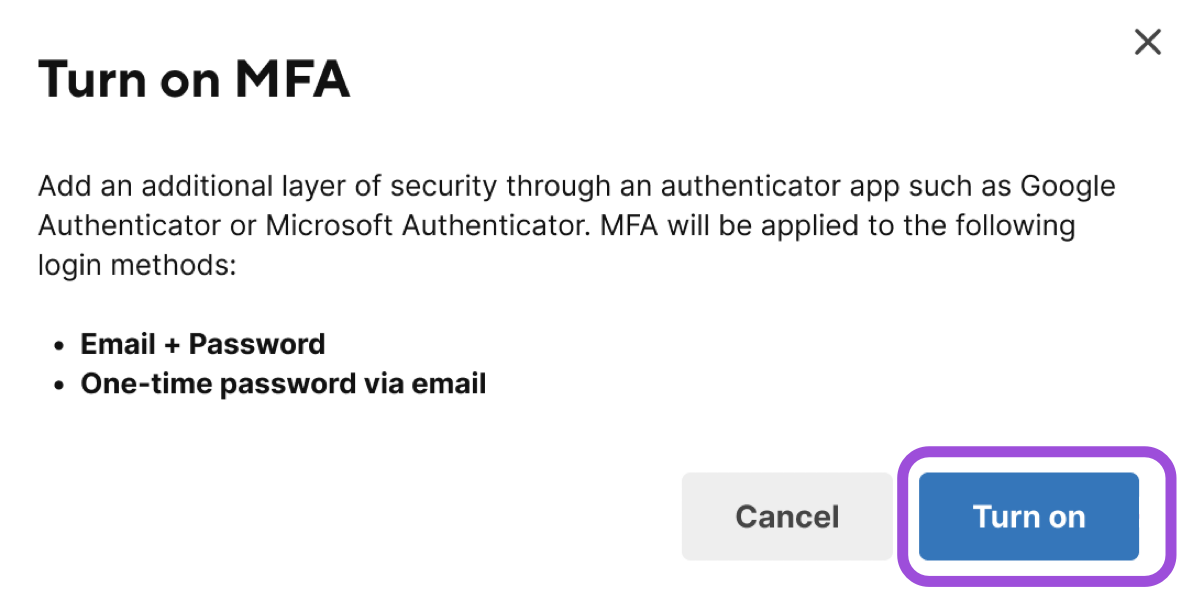
Enterprise plans
Domain-level enforcement
- Go to Admin Center and select the Menu icon in the upper left.
- Navigate to Settings > Authentication.
- Scroll to the One-time password via email section.
Toggle on Multi-factor authentication.
Brandfolder Image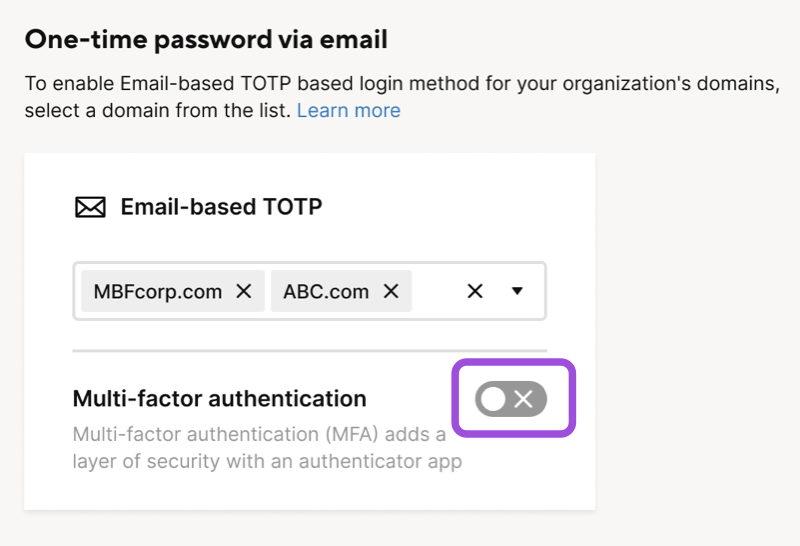
Select Turn on to confirm the action.
Brandfolder Image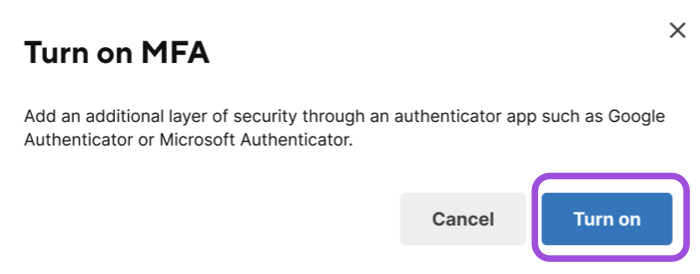
Enable MFA as a back-up sign-in option for System Admins.
Plan-level enforcement
- Go to the Admin Center homepage.
- Scroll to the Settings section and identify the Authentication card.
Select Multi-factor authentication (MFA).
Brandfolder Image
On the Authentication page, select MFA (authenticator app).
Brandfolder Image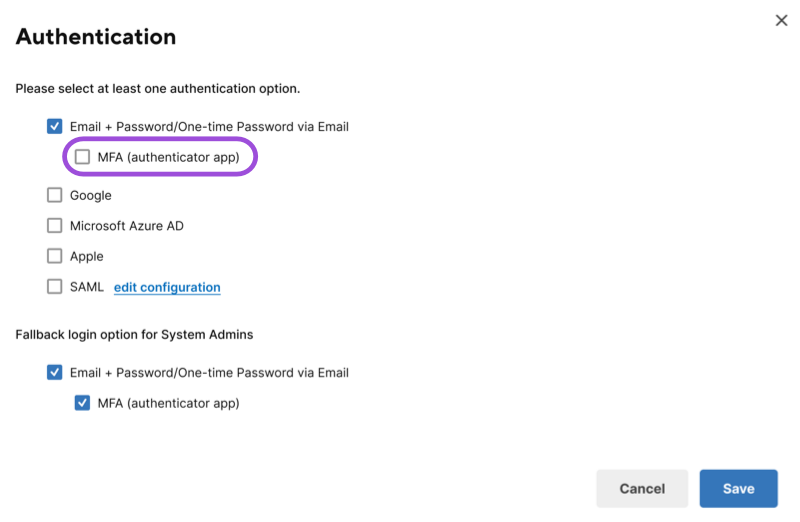
Select Save to apply the changes.
Enable MFA as a back-up sign-in option for System Admins.
Things to consider
User deactivation
If you deactivate a user, your plan retains their MFA enrollment data. Upon reactivation, that user can sign in with their existing MFA setup without needing to re-enroll.
User removal
If you remove a user from your plan or domain, either manually or via SCIM/Directory, their MFA enrollment gets deleted. If they receive an invitation later, they must complete the MFA enrollment process again.
User merge process
When you merge a user into another user account, the MFA device enrollment from the original (source) user account gets deleted. The target (merged) user account doesn’t inherit MFA setup from the source user.
If you enforce MFA for the merged user's domain or plan, they must complete a one-time MFA setup again during their next sign-in attempt.