The email-based time-based one-time passcode (TOTP) login method generates a one-time temporary code and sends it to the user’s email for each login attempt. The user must enter the code received to sign in to Smartsheet successfully.
Unlike the traditional password login method, the email-based TOTP significantly minimizes the possibility of phishing attacks, password theft, or intruder threats. This is because email-based TOTP requires users to access their email to obtain their temporary code, therefore adding an extra layer of security that’s more challenging for attackers to compromise.
USM Content
For troubleshooting help, see Troubleshooting: Email-based TOTP. For details on how TOTP interacts with user provisioning, see Admin Center: Automatically add users with UAP.
Password-based login deprecation
Smartsheet plans to remove the ability for users to log in via password-based authentication. Smartsheet will communicate the cutoff date well in advance once the timing has been finalized. Until then, the existing password-based login fallback mechanism remains the same.
What users see
When email-based TOTP is enabled for your domain, users see a prompt to enter a one-time passcode after they provide their email address on the Smartsheet login screen. Smartsheet sends a temporary code to their email, and they enter it to complete the sign-in process.
For details on common issues users encounter during sign-in, such as delayed emails, expired codes, or lockouts, see Troubleshooting: Email-based TOTP.
Things you should know
Known limitations
- Email-based TOTP doesn't support the User Auto-Provisioning feature.
- To sign in with TOTP, users must have previously set a password for their Smartsheet account and accepted the User Agreement. New users only receive their TOTP after completing these steps.
- By default, TOTPs are only valid for 10 minutes. System Admins can’t edit this setting.
- If a user incorrectly enters the code three consecutive times, they must wait 10 minutes to request a new TOTP.
- The email-based TOTP doesn’t change any existing single sign-on (SSO) methods, such as Google, Microsoft, or Apple; instead, it serves as an additional login option.
- This feature is only available in version 25.4 of the Smartsheet mobile app.
Email-related considerations
- If you've configured email filters that block Smartsheet emails coming from system@system.smartsheet.com, users won’t be able to receive their TOTP through email.
- If users end up receiving multiple TOTPs because of delays in email delivery, note that those codes don’t expire as soon as a new one is requested, following the 10-minute expiry. However, it is recommended that they always use the latest one they’ve received.
Manage email-based TOTP login across your domains
For non-Enterprise plans, all supported login methods (including email-based TOTP) are enabled by default and can't be individually deactivated.
Enterprise plans have the flexibility to choose which login methods to enable. Smartsheet supports this at two levels: plan-level and domain-level.
Here's what you need to know as System Admin of an Enterprise plan:
- At the plan level, the activation and deactivation of password-based and email-based TOTP login methods are interconnected. It’s impossible to activate email-based TOTP while disabling the password-based login method. If you simply wish to enable TOTP for your domain, you must follow the steps on activating email-based TOTP login at the domain level.
- Email-based TOTP is automatically enabled for Enterprise plans where the traditional password login method is currently active at the plan level.
- In Enterprise plans where the password login method has been previously deactivated, email-based TOTP is also be disabled by default. However, System Admins of those plans can choose to activate both login methods simultaneously at the plan level if needed.
Activate email-based TOTP login at the domain level
- In Admin Center, select .
- Navigate to Settings > Authentication.
Scroll down to the One-time passcode via email tile and use the Select domain drop-down menu to add email-based TOTP to any listed domains. Validated and activated domains automatically populate.
Brandfolder Image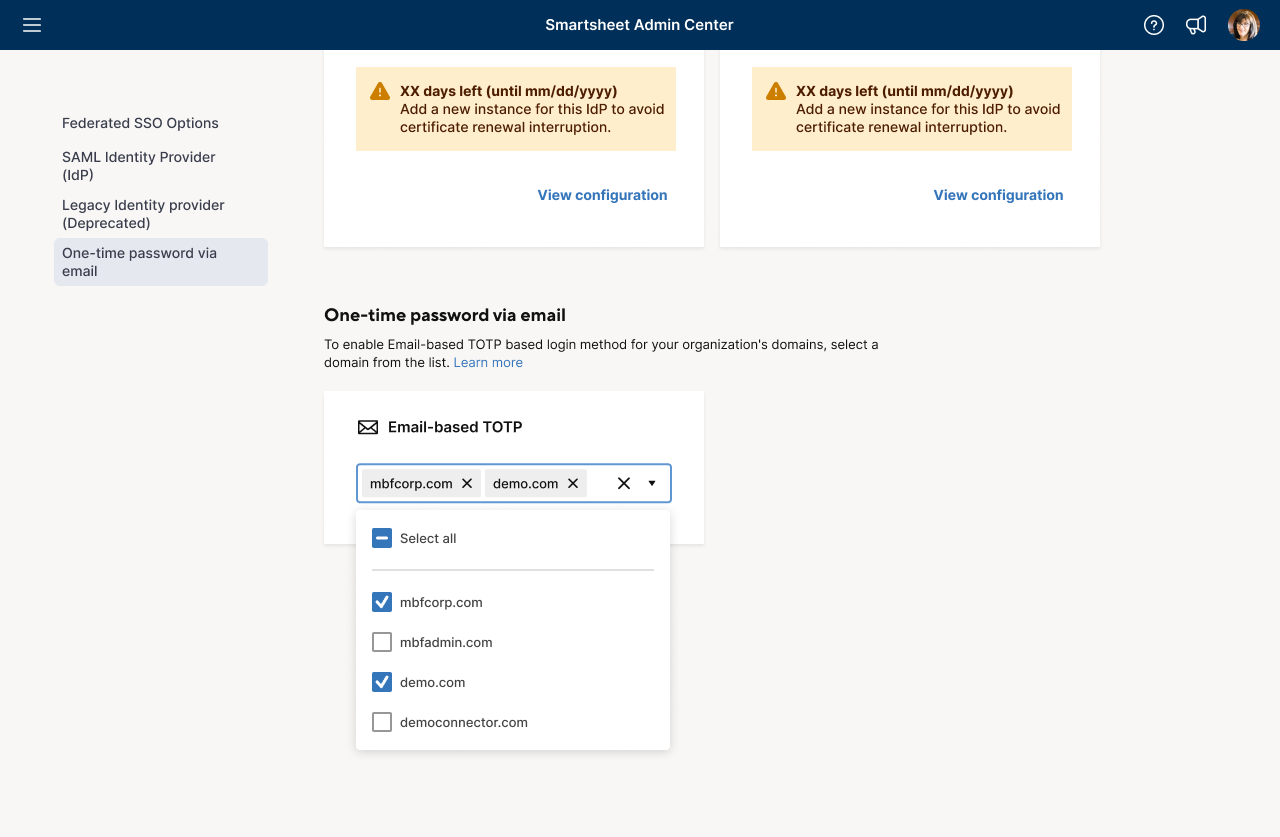

Deactivate email-based TOTP login
- In Admin Center, select .
- Navigate to Settings > Authentication.
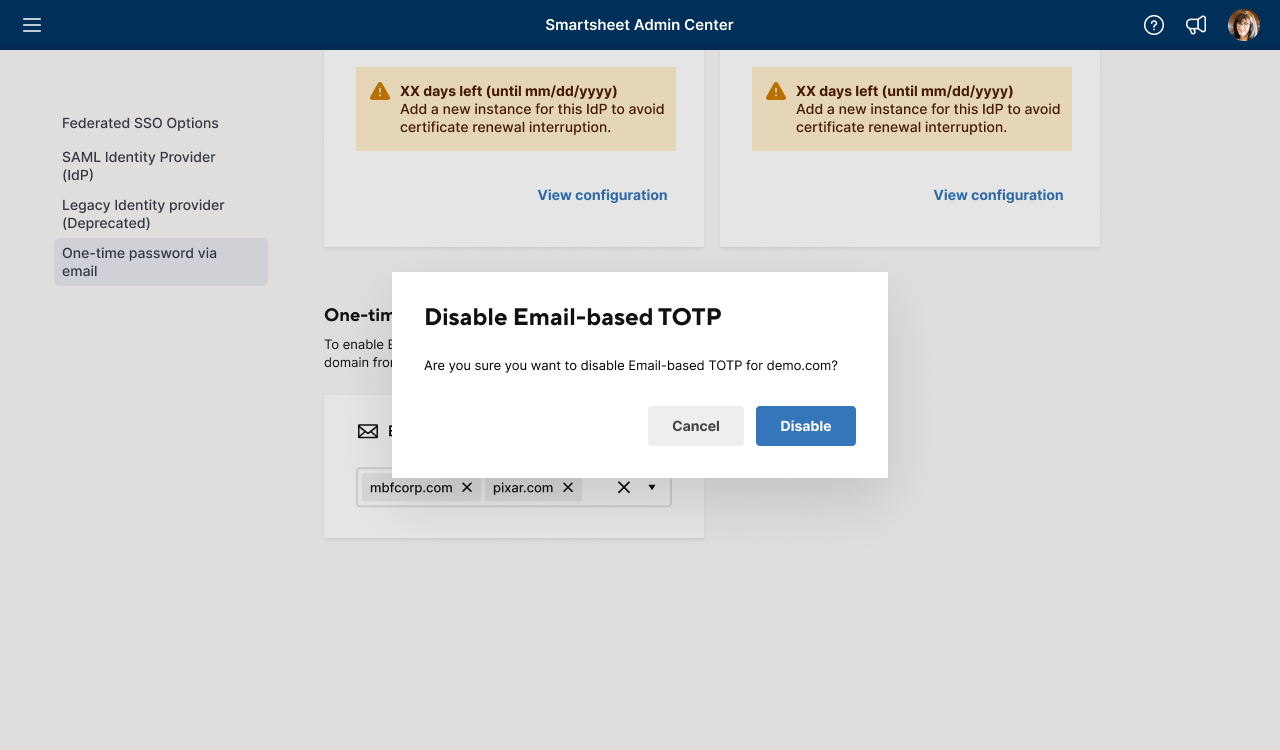
- Scroll down to the One-time passcode via email tile and use the Select domain drop-down menu to remove email-based TOTP for any listed domains.
Select Disable.
Brandfolder Image